
Healthcare BPO: How to Outsource Without Compromising HIPAA Compliance
Choosing the right BPO for healthcare organizations means balancing efficiency with something that can’t be compromised: patient privacy. A healthcare BPO handles calls, documentation, or direct patient support, which means it also becomes part of your compliance picture. Pick the wrong healthcare BPO services provider, and you’re not just risking service quality, you’re risking legal, financial, and reputational exposure.
Here’s what healthcare BPO outsourcing actually requires from a compliance standpoint, what happens when it goes wrong, and how to vet a partner before signing.
How to be HIPAA compliant as a BPO partner
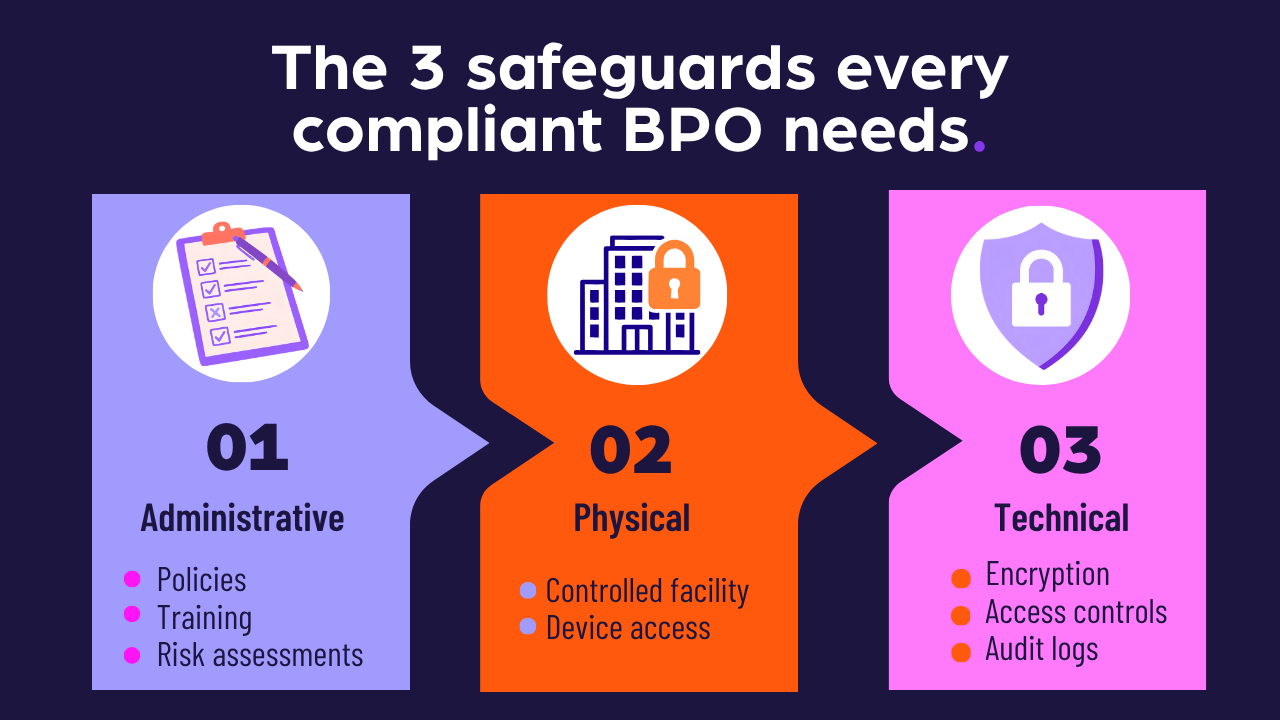
In plain terms: every process, system, and person who comes near Protected Health Information (PHI) needs real controls around it, not just a policy PDF nobody reads. That means access limited to what people actually need for their job, encryption, ongoing training, and a signed Business Associate Agreement (BAA) that spells out who’s responsible for what.
And here’s something people often miss: PHI isn’t just digital. It’s spoken out loud on calls, written on forms, stored in systems. A good healthcare BPO treats all of it the same way.
The risk of choosing a non-compliant BPO
Picking the wrong vendor can cost a lot more than the contract itself. Think corrective action plans, regulatory monitoring, fines, and legal liability, since business associates can be held directly responsible too. Add in the reputational hit of a breach, and it’s easy to see why this isn’t a corner to cut.
Case in point: MMG Fusion, a HIPAA business associate, had a breach that hit around 15 million people after HHS found gaps in their risk analysis and notification process. They ended up settling with HHS in March 2026 and are now under a three-year corrective action plan. That’s the real cost of outsourcing to the wrong partner.
What to ask before you sign
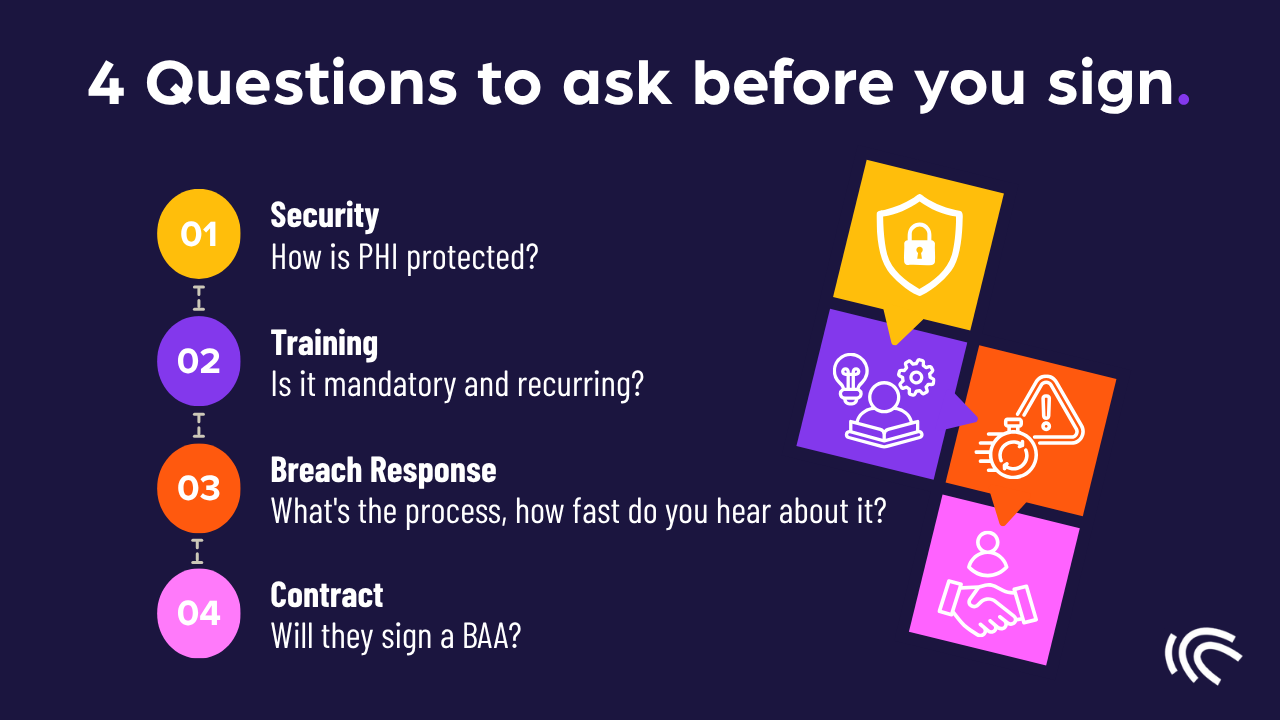
Skip the yes-or-no question (“Are you HIPAA compliant?”) and ask them to actually show you: how they protect data, how they train people, and what happens when something goes wrong. If they can’t back it up with evidence, take that as your answer.
How ICC delivers healthcare BPO outsourcing you can trust
For us, compliance isn’t a once-a-year training and a binder on a shelf. It’s daily checklists, credential-access oversight, live monitoring, and full HIPAA recertification anytime a concern comes up. Training gets renewed annually and reinforced monthly. And an independent partner audits the whole program from the outside, so it’s not just ICC grading its own homework.
That’s what a HIPAA compliant BPO actually looks like day to day, not just on a compliance page.
Ready to see it in action? Explore how we support different industries, or let’s talk directly about building a tailored outsourcing solution you can actually trust.